A second Temu DSA breach case is now on the table after the European Commission concluded on 17 November 2026 that the online marketplace has failed to stop illegal and unsafe products from reaching European shoppers. The preliminary finding targets Temu’s duty under Article 35 of the Digital Services Act to put reasonable, proportionate and effective risk mitigation measures in place.
The timing of the Temu DSA breach finding matters. Only in May 2026 the Commission fined Temu €200 million for an inadequate risk assessment, and in October it approved the action plan the company submitted to fix that problem. The new case moves the focus from how Temu describes its risks to what it actually does about them.
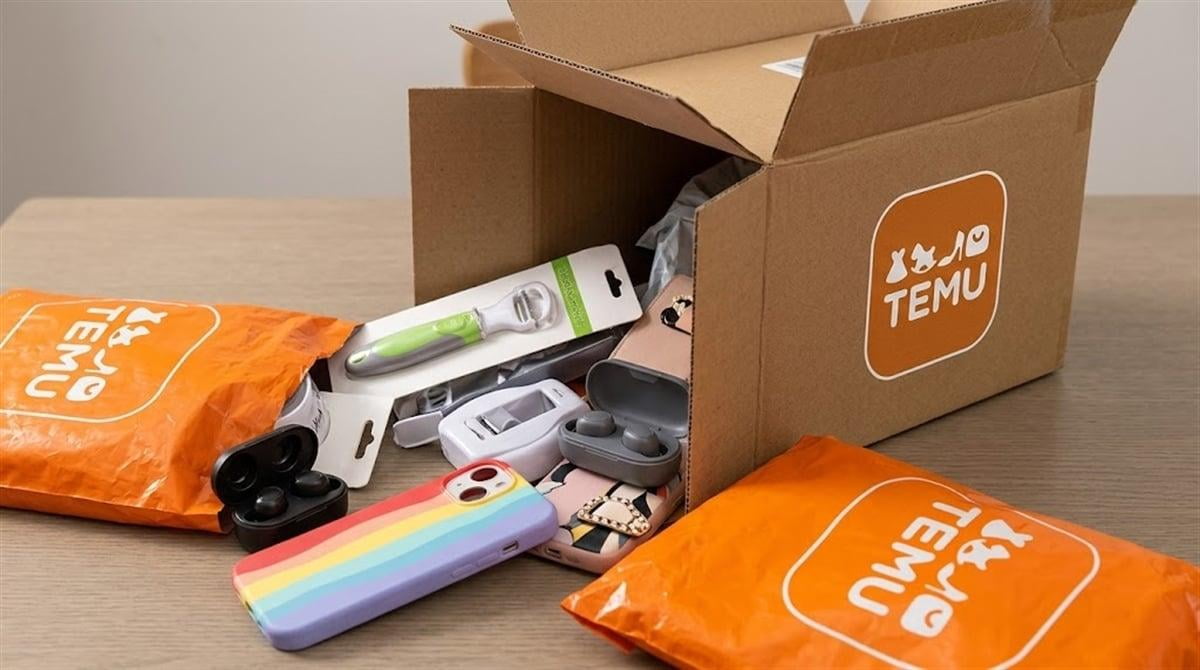
Investigators trace the Temu DSA breach to three weak points. Sellers must supply test reports for only a very small share of products, and Temu often does not check the reports it receives. High-risk categories such as toys, electronics and cosmetics do not get priority in physical checks, and inspections have not kept pace with the growth in listings.
Content moderation forms the second weak point. According to the Commission, Temu’s system mainly screens listing details and compliance with its own terms of service rather than product safety. Its tools for comparing new listings with previously flagged items pay too little attention to dangerous goods, and the number of human moderators has not grown in line with the catalogue.
The third weak point lies in sanctions. Temu penalises individual stores rather than the traders behind them, so a trader whose store closes can keep selling through other storefronts. Traders can also commit many serious infringements before Temu suspends anything, which the Commission says offers little deterrence.
Henna Virkkunen, the Executive Vice-President for Tech Sovereignty, Security and Democracy, framed the case in consumer terms, saying that shopping online should not mean risking illegal and unsafe products. That message lands as EU customs authorities already struggle with billions of low-value parcels arriving each year, many of them sold through marketplaces such as Temu, which PDD Holdings owns.
Temu rejects the conclusions on the alleged Temu DSA breach. The company says it respectfully disagrees, that it invests significantly in compliance infrastructure and human expertise, and that it expects to reach an amicable resolution with the Commission. It can now examine the investigation file and reply in writing.
The procedure gives both sides room before any penalty. The Commission will consult the European Board for Digital Services, and if it confirms the Temu DSA breach it can adopt a non-compliance decision. Such a decision may carry a fine of up to 6% of the company’s worldwide annual turnover and an order to change its practices.
The wider proceedings, opened in October 2024, still cover addictive design, recommender systems and researcher access to data. A confirmed Temu DSA breach on product safety would strengthen the Commission’s hand on those open questions as well.
For Brussels, the case tests whether the Digital Services Act can deliver results on physical goods and not only on online content. A firm outcome on the Temu DSA breach would tell every large marketplace that test reports, moderators and trader-level sanctions are legal obligations in the EU, not optional extras.