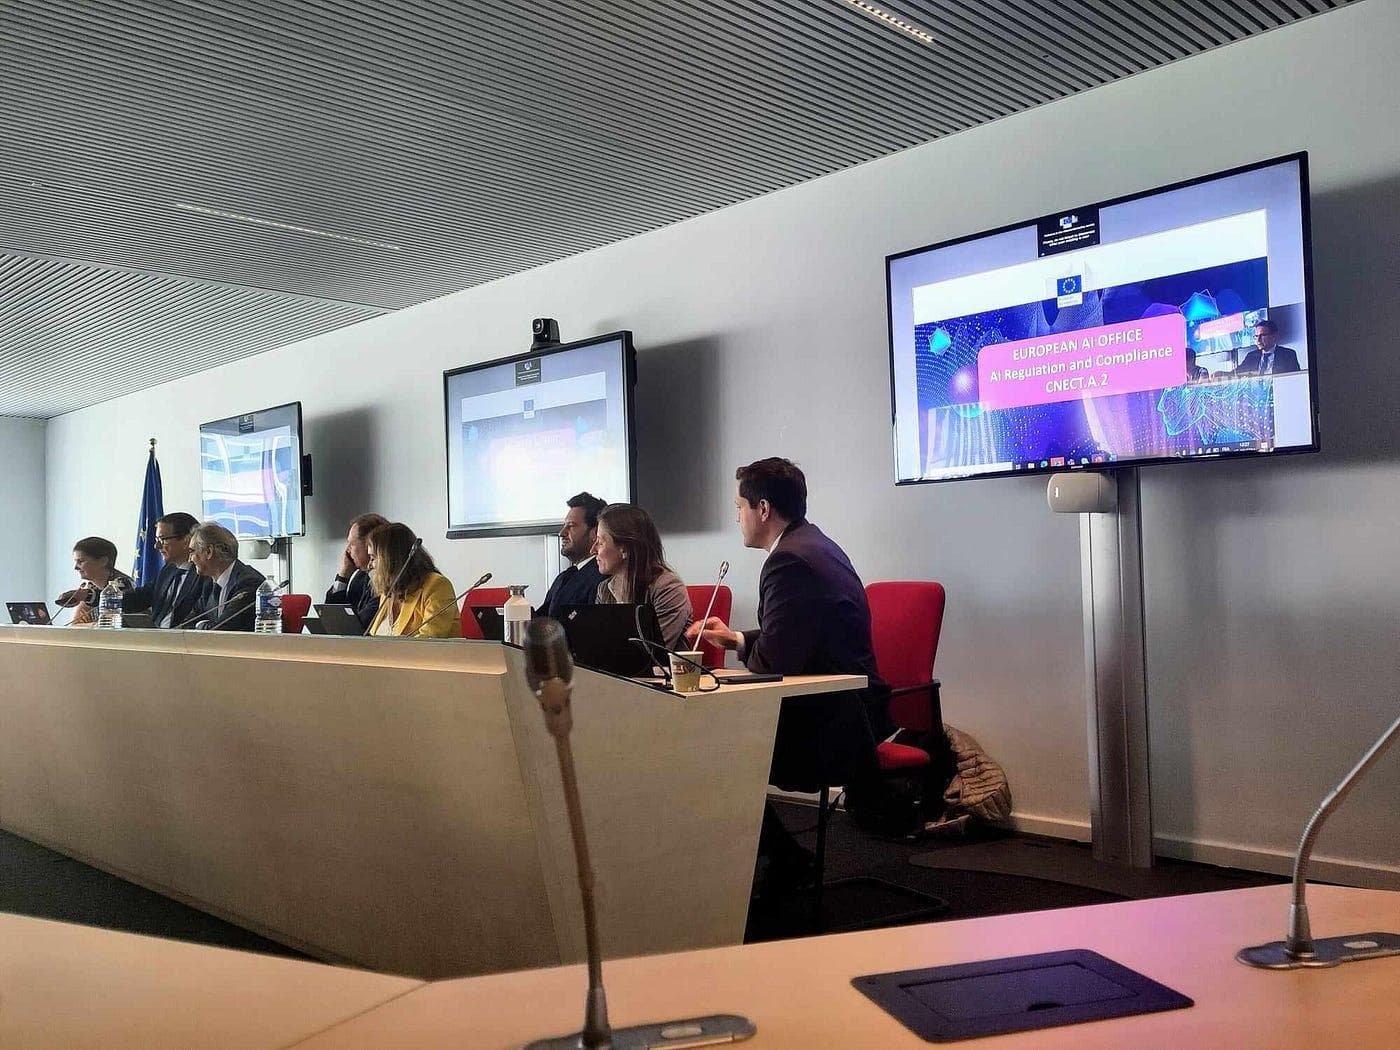
Brussels: The traveller data agreement with the United States is moving through the European Parliament with the Commission asking for provisional application this year, and MEPs and data protection officials say the safeguards are not yet strong enough. The Commission presented the draft on 10 September 2026 after governments gave a negotiating mandate in December 2025.
The stakes are practical: Washington links continued visa-free travel for Europeans, up to 90 days, to an Enhanced Border Security Partnership due by the end of 2026.
What the traveller data agreement covers
The traveller data agreement is not itself a legal basis for sending personal data. Each exchange would depend on separate bilateral arrangements between the United States and individual member states, setting out national systems, data categories, procedures and volume limits. The process has two stages. An automated query based on biographical data, a national identity number or fingerprints returns a match, basic identity data and possibly a photo. A more detailed second request requires human assessment.
Commission official Olivier Onidi told the civil liberties committee on 5 November that the traveller data agreement would handle only a few hundred queries a day and would cover entry, meaning border checks, travel authorisation and visa applications. Denmark is excluded, and Ireland is covered only if the EU later notifies Washington.
Why data protection officials want stronger safeguards
On 29 October, European Data Protection Supervisor Wojciech Wiewiórowski said this would be the first time the EU shares personal data, including biometrics, with a third country at such scale for border control. He called for real oversight on both sides of the Atlantic.
His office recommends careful selection of national source systems, a clear list of offences that could count as a public order or security risk, and an objective link between each request and the cited risk. It also wants onward sharing notified to the transmitting authority, US supervisory authorities named before any provisional application, and a Commission check that judicial redress is effective for all nationalities.
Commentators add further concerns: automated decisions with significant adverse effects are not absolutely barred where national law allows, transparency may amount to a general notice, and special categories of data such as political opinions or religion can be transferred when particularly relevant.
The public order question before MEPs
Onidi argued that the Commission would detect misuse of the term public order very quickly, and that the safeguard would operate afterwards rather than through a narrower definition in the text. He rejected the supervisor’s request for a justification before the initial automated query, because an automated step cannot express one.
Birgit Sippel of the Socialists and Democrats asked the Commission to map data already shared through passenger name records, the terrorist finance tracking programme and Europol. Raquel García Hermida-van der Walle of Renew called the public order concept the key point. Their questions show that the traveller data agreement will be judged against the existing web of transatlantic data deals, not in isolation.
What happens next
The Council must authorise signature and provisional application, and Parliament must give consent before formal conclusion. Onidi said the aim is provisional application this year so that Washington can open bilateral talks with member states, and he admitted the EU is a bit over time.
The pressure of the visa-free deadline gives Parliament leverage over the traveller data agreement. A concrete mapping of existing data flows, named US supervisors and tighter language on public order would let consent move faster. Without them, the traveller data agreement risks a repeat of earlier transatlantic data disputes, which ended in court.