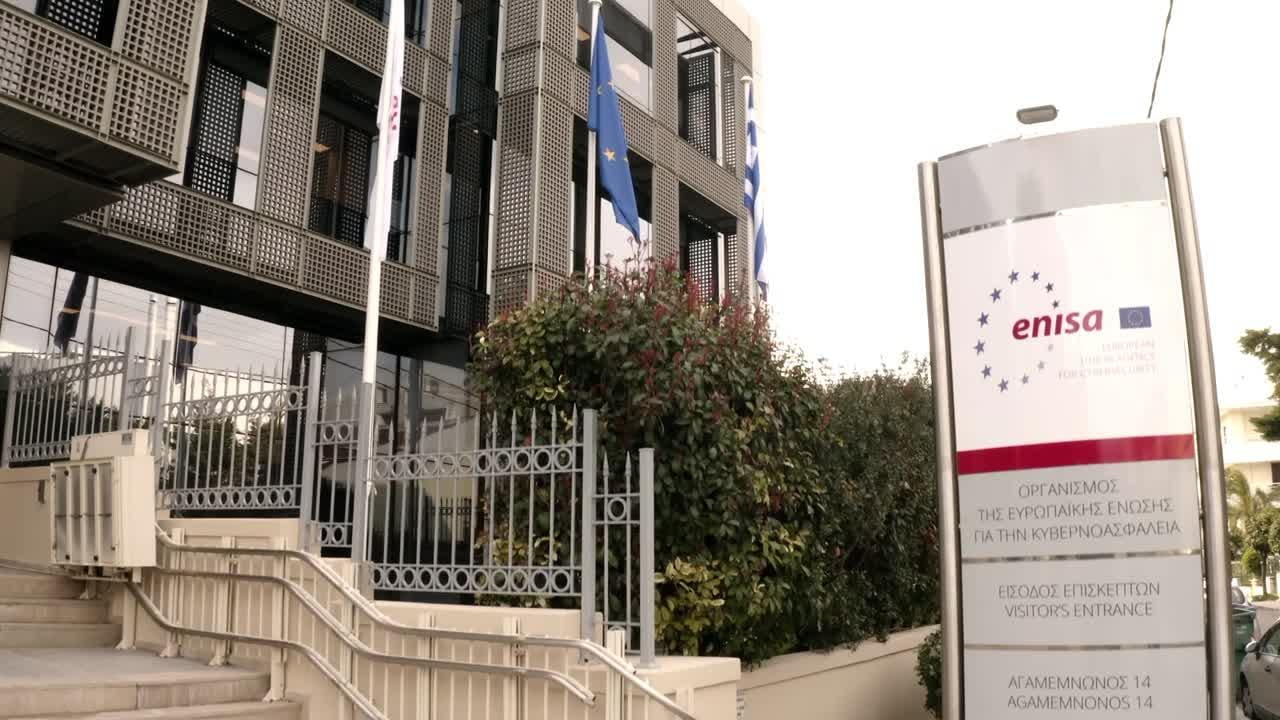
Athens: The agency that will receive Europe’s vulnerability reporting sits in a city better known for exporting philosophy than deadlines. Since 11 September, ENISA has been running the Single Reporting Platform, and manufacturers of products with digital elements now owe it a notification within 24 hours of learning that a vulnerability in their product is being actively exploited.
The clock is the story. Article 14 of the Cyber Resilience Act sets three stages. An early warning goes out within 24 hours. A fuller notification, describing the flaw and any corrective or mitigating measures, follows within 72 hours. A final report lands within 14 days, covering the vulnerability, the actors involved where they are known, and the fix. Severe incidents affecting the security of a product run on a parallel track.
Read the Commission’s own guidance and the design intent is clear. One report, one platform, automatic routing to the relevant national CSIRT and to ENISA. Manufacturers stop filing the same facts in five formats. Authorities stop discovering the same exploited flaw at five different speeds.
The scope clause that catches everyone
The obligation does not wait for new products. It applies to products already placed on the EU market, which means a manufacturer cannot exit the regime by freezing its catalogue. Anything shipped years ago and still supported is inside.
That single drafting choice converts a compliance project into an inventory problem. To report within 24 hours, a company must know which of its products contain the affected component, which versions remain in the field, and who inside the organisation is authorised to declare that exploitation is active rather than theoretical. Firms with a mature product security incident response function already hold those answers. Firms that treat security as a release-time checklist do not, and they will discover the gap on the day a researcher publishes proof-of-concept code at 23:00 on a Friday.
The judgement call is harder than the paperwork. Active exploitation is a factual threshold, but the evidence often arrives as a partial telemetry signal or a customer report that cannot be confirmed for days. Report early and a manufacturer may notify authorities of an incident that never was. Report late and it misses a statutory deadline that regulators can verify from the platform’s own timestamps. Most legal teams will resolve that asymmetry by over-reporting, at least in the first year.
What the first year will actually measure
ENISA gains something it has never had, which is a continuous, structured feed of exploited vulnerabilities across consumer and industrial products in a single market. The analytical value of that feed is considerable. The operational value depends on whether national CSIRTs have the staff to act on volume rather than file it.
Enforcement is the quieter variable. Market surveillance authorities differ sharply in capacity across the 27, and the reporting duties arrived more than a year before the Act’s full compliance date in December 2027. That sequencing is deliberate. It gives authorities a live picture of who is paying attention before the broader essential requirements bite, and it gives manufacturers a rehearsal period in which mistakes are cheaper.
Vendors selling into critical infrastructure will feel the change first, because their customers now have a documentary record to ask about. Procurement teams can demand evidence that a supplier filed on time. That contractual pressure, not the statutory penalty, is likely to do most of the disciplining. The platform launch was treated as an administrative milestone. It is closer to a public audit of which manufacturers actually know what they shipped, and the first 24-hour report from a firm that does not will make the point better than any regulator could.